The Shield
Cloud Security & Compliance
Your roadmap isn’t slipping, it’s collapsing. Every day without SRE cover compounds risk: outages, burnout, and missed deadlines. Hire slow, fail fast. Air Cover buys survival time.
The Challenge
Security Without Structure Doesn’t Scale
Security isn’t failing because you lack tools, it’s failing because it’s fragmented. As systems grow, gaps widen. Without embedded controls and governance, compliance becomes reactive, and risk becomes harder to manage.
Fragmented Security Controls
Security tools exist, but they’re disconnected. Inconsistent policies across systems create blind spots and make enforcement unreliable.
Manual Compliance Effort
Audits rely on manual checks and scattered evidence, slowing teams down and making compliance a time-consuming, repetitive process.
Weak IAM Governance
Access grows without structure. Over-permissioned users and unclear ownership increase risk and make control harder to enforce.
Limited Visibility Across Systems
No single view of security posture. Issues go unnoticed, responses are delayed, and teams lack clarity on what needs attention.
Reactive Security Practices
Security is addressed after issues appear, not built into workflows, leading to repeated fixes and inconsistent protection.
Scaling Without Security Alignment
As infrastructure grows, security doesn’t keep up. Gaps expand, complexity increases, and maintaining compliance becomes harder.
The Solution
Built for Compliance, Without Slowing You Down
SOC2, ISO27001, and local regulations shouldn’t feel like a scramble. We harden your infrastructure with the right controls, policies, and automation, so you’re always secure, compliant, and ready for audit.
Compliance-Ready Architecture
We design and structure your infrastructure to meet SOC2, ISO27001, and local regulations, so compliance is built in, not bolted on later.
Security Controls & Governance
We implement IAM, policies, and security controls across your environment, so access is controlled, risks are reduced, and standards are enforced consistently.
Automated Compliance & Monitoring
We integrate scanning, monitoring, and reporting, so you stay continuously compliant, detect issues early, and pass audits with confidence.
GET A FREE CONSULTATION
+65 60288048
Ready to be audit-ready without the last-minute scramble? Get your infrastructure aligned with SOC2, ISO27001, and local regulations before compliance becomes a blocker.
Core Capablities
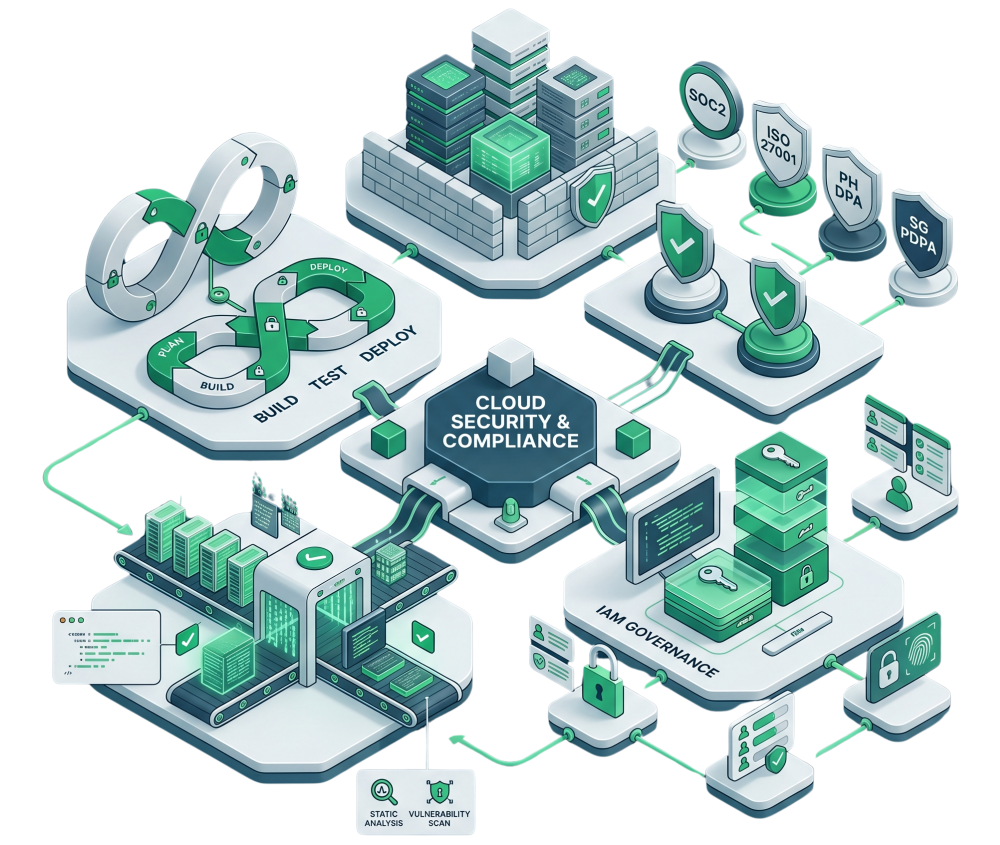
Security Built Into Every Layer
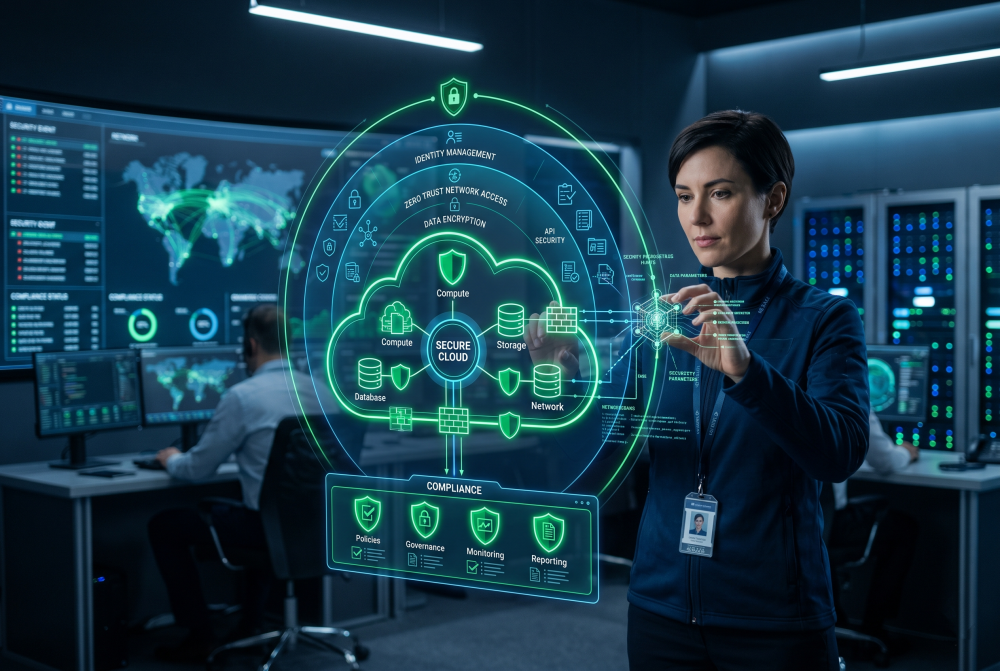
We embed security into how your systems are built and run, so protection, visibility, and control scale naturally with your infrastructure, without slowing your teams down.
Security is built into your pipelines and workflows, so every change is tested, validated, and deployed with protection already in place.
IAM Governance
We design and enforce structured access controls, so the right people have the right access, reducing risk while keeping operations efficient.
We implement continuous scanning across code and infrastructure, so vulnerabilities are detected early and resolved before they impact production.
From Risk to Readiness, Security That Scales With You
Security shouldn’t slow you down. We embed protection, compliance, and governance into your cloud, so you stay secure, audit-ready, and confident as you grow across environments.
Assess
Evaluate Your Posture
We review your infrastructure, access controls, and policies, so you understand your current security posture and compliance readiness clearly.
Design
Define Secure Architecture
We design security-first cloud environments, so controls, policies, and compliance requirements are built in, not added later.
Implement
Enforce and Automate
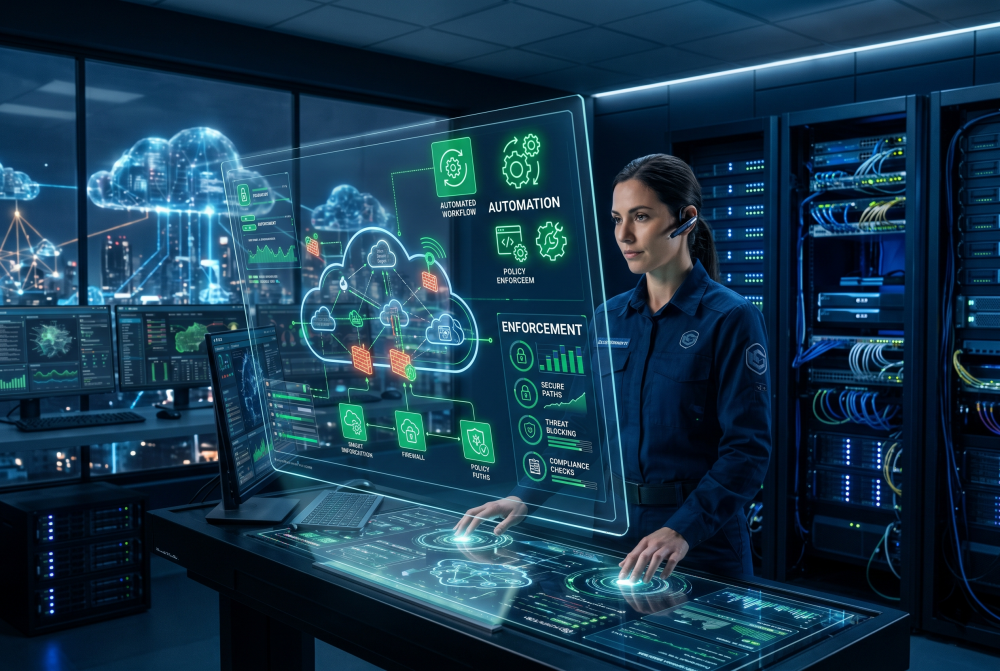
We deploy security controls, IAM governance, and automated scanning, so protection is consistent, scalable, and always active.
Assure
Monitor and Maintain Compliance
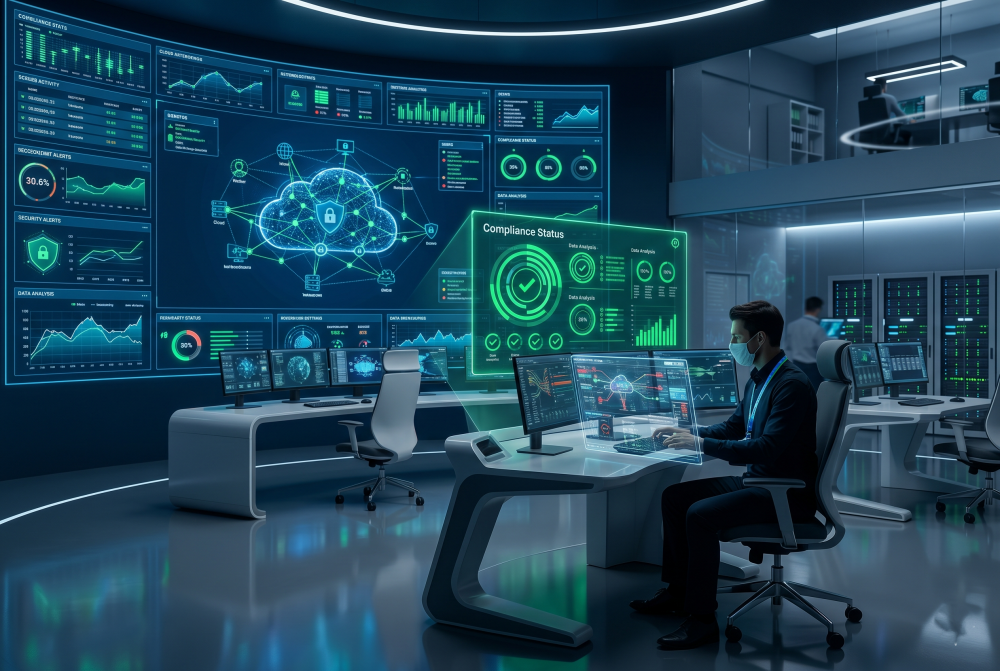
We continuously monitor, audit, and refine, so you stay compliant, secure, and prepared for audits without disruption.
Frequently Asked Questions
Answers to common questions about cloud security, compliance, governance, IAM, and security automation.
What does CDOps Tech’s Cloud Security & Compliance service cover?
Our Cloud Security & Compliance service helps organizations strengthen their cloud security posture and build compliance into their infrastructure. This includes security architecture, IAM governance, security controls, compliance policies, automated security scanning, monitoring, and ongoing compliance management.
Can you help us prepare for SOC 2 or ISO 27001 compliance?
Yes. We help design and structure cloud infrastructure around requirements such as SOC 2 and ISO 27001. This includes identifying control gaps, implementing appropriate security policies and access controls, automating monitoring and evidence collection, and building compliance into your engineering workflows rather than treating it as a last-minute audit exercise.
How do you improve security without slowing down our development teams?
We integrate security into existing engineering workflows instead of adding manual approval steps wherever possible. Through DevSecOps practices, automated security checks, policy enforcement, and continuous scanning, security becomes part of the development and deployment process without creating unnecessary friction for developers.
Can you assess our existing cloud security posture?
Yes. We begin by assessing your infrastructure, access controls, security policies, and existing security practices. This helps identify misconfigurations, control gaps, access risks, and compliance weaknesses, giving you a clear picture of your current security posture and the improvements needed.
How do you manage IAM and access controls?
We establish structured identity and access management practices based on roles, responsibilities, and least-privilege principles. We review existing permissions, identify excessive or unnecessary access, clarify ownership, and implement controls that provide the right people with the right level of access while reducing security risk.
Does The Shield include automated security scanning?
Yes. We can implement continuous security scanning across code and cloud infrastructure to identify vulnerabilities and configuration issues early. Integrating these checks into development and deployment workflows helps teams address security issues before they reach production.
How do you keep cloud environments continuously compliant?
Compliance needs to be maintained continuously as cloud environments, workloads, and configurations change. We use automated monitoring, security controls, policy enforcement, scanning, and reporting to identify drift and potential issues early, helping teams maintain compliance rather than preparing for it only when an audit is approaching.
What does the Assess, Design, Implement, and Assure process involve?
We first assess your current infrastructure, access controls, policies, and compliance posture. We then design a security-first architecture, implement the required controls and automation, and continuously monitor and refine the environment. This approach helps security and compliance remain aligned with your infrastructure as it evolves.